Test how visually subtle backdoors survive federated training. FiBA adapts invisible trigger families to a shared benchmark and compares their success, clean-model utility and detectability. A separate LSB experiment asks whether placing a trigger in low-activation image regions changes that tradeoff.
LSB500 / LSB700 · Low regions · High regions · Unmasked
1 / 6
What this adds
01
A federated comparison: evaluate LSB, WaNet, Encoder and LIRA attacks alongside visible BadNet under controlled client participation.
02
Expose defense tradeoffs: compare attack success with clean accuracy for the tested aggregation rules and attack configurations.
03
Probe attention-based placement: compare low, high and unmasked LSB triggers, including both perceptual distance and model anomaly scores.
Abstract
Federated Learning (FL) enables collaborative training of machine learning models across multiple devices, while preserving data privacy. However, it also introduces vulnerabilities to backdoor attacks, where malicious updates can corrupt the global model. This work focuses on the largely unexplored domain of Federated invisible Backdoor Attacks (FiBAs), which use visually indistinguishable triggers to manipulate model behavior without being detected. We investigate the feasibility and effectiveness of these attacks, considering the unique challenges posed by FL, such as limited local training time and the need for model update aggregation. Our study presents a comprehensive evaluation of the attack success rate (ASR) of invisible BAs under various settings and defenses. Based on our observations, we propose a backdoor trigger hiding technique based on low model attention regions to improve attack resilience in federated settings. Our findings provide critical insights into the optimization of invisible BAs in FL and highlights the need for robust defense mechanisms to safeguard FL systems.
Use ResNet-18 on CIFAR-10 and CIFAR-100 with nonoverlapping, non-IID client data. Malicious clients learn a common target from poisoned samples while honest clients train normally. Coordinated attackers share the required trigger string, warping field, encoder or pretraining resources for their attack family.
Sections 3.1 and 4, PDF pages 5–9. Main settings: 10 clients, 100 rounds, five local epochs, Dir(0.5) and poison rate 0.5. This is an evaluation study, not a new defense.
02
Compare one aggregation rule at a time
The defense grid compares FedAvg, Median, Trimmed Mean, FoolsGold, KRUM and Multi-KRUM under fixed attack conditions. Each rule can change both backdoor success and clean accuracy. Model replacement and distributed triggers are additional probes with their own assumptions.
Table 2 and Figures 3–6, PDF pages 11–14. The defense grid has BadNet, LSB, WaNet and Encoder rows; it does not include LIRA or report a PCA column.
03
Keep the evaluation axes separate
Attack success rate is the proportion of poisoned non-target test samples classified as the target. Clean accuracy measures ordinary utility; LPIPS and Neural Cleanse anomaly scores measure different aspects of detectability. Reported ± values are retained exactly because the paper does not define their dispersion statistic or run count.
Section 4 and Tables 1–3, PDF pages 9–11 and 14. These measurements do not establish statistical significance or a universal failure of robust aggregation.
04
Test low-activation placement specifically for LSB
A RankMe-type embedding score checks convergence before SmoothGradCAM++ maps are accumulated. The experiment compares reported low-, high- and unmasked placement for LSB500 and LSB700. Concentrating changes can also alter trigger intensity, so the comparison does not isolate attention from every other factor.
Section 3.2, Algorithm 1, Table 3 and Figure 7, PDF pages 7–8 and 14–15. Prose and mask-ordering descriptions differ; placement labels are preserved as reported. WaNet and LIRA attention placement remain future work.
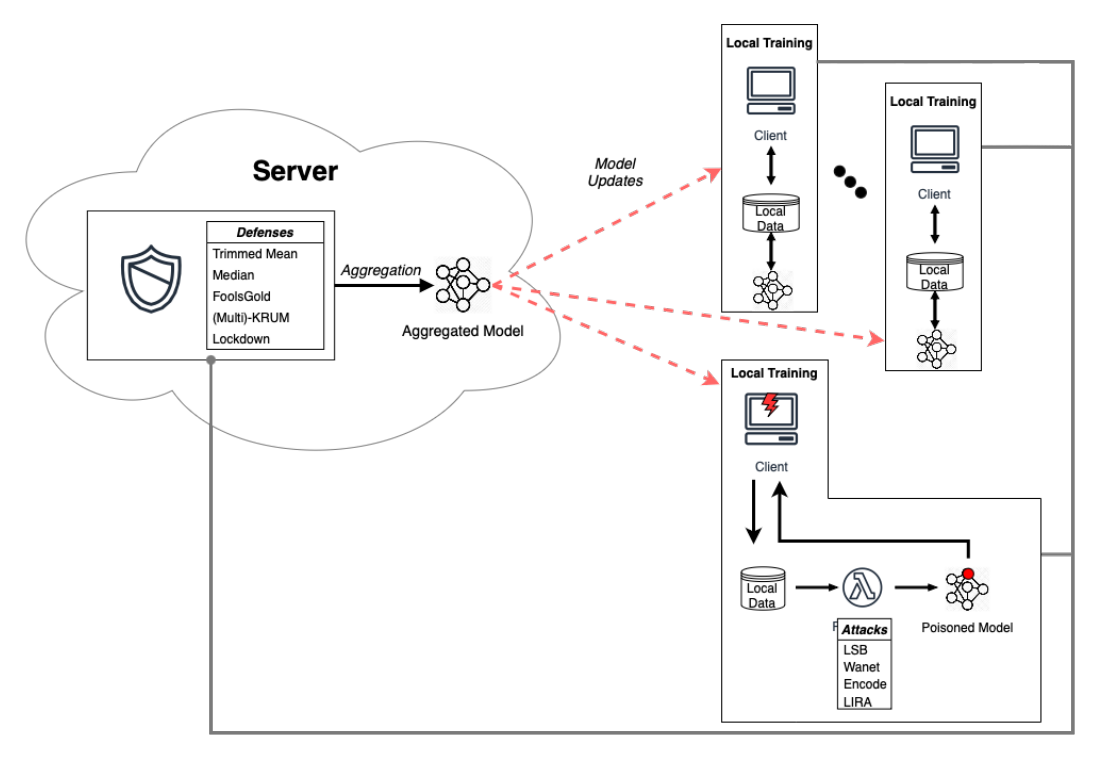
Original paper figures & sourcesEnlargeBackdoor triggers enter during local training, while the server applies defenses when combining client updates. The study measures how this interaction shapes invisible attack success. Figure 1 in the accepted manuscript (PDF page 5) Evaluation
Results
More attackers, greater success
CIFAR-10 · ResNet-18 · 10 clients
Attack success rate (%)
ASR, 10% attackers (%)ASR, 20% attackers (%)
050100
BadNet (visible)
ASR, 10% attackers (%): 94.96 ± 0.81
ASR, 20% attackers (%): 97.52 ± 0.40
LSB
ASR, 10% attackers (%): 41.59 ± 6.19
ASR, 20% attackers (%): 65.43 ± 3.93
WaNet
ASR, 10% attackers (%): 44.41 ± 3.50
ASR, 20% attackers (%): 82.05 ± 3.59
Encoder
ASR, 10% attackers (%): 29.44 ± 5.90
ASR, 20% attackers (%): 88.59 ± 4.01
LIRA
ASR, 10% attackers (%): 10.52 ± 1.22
ASR, 20% attackers (%): 41.57 ± 4.66
Attention placement has a cost
LSB700 · CIFAR-10 · 10% attackers
Low attention is easier to exploit and detect. CIFAR-10, LSB700, 10% attackers; compare no activation mask with low- and high-attention masks. ASR is a percentage; LPIPS and Neural Cleanse anomaly index are unitless. Higher anomaly index means easier detection; the discussed threshold is 2.
@inproceedings{marinus2025invisible,
  title = {On the Effectiveness of Invisible Backdoor Attacks in Federated Learning},
  author = {Marinus, Mattjis and Tsouvalas, Vasileios and Meratnia, Nirvana},
  booktitle = {Ubiquitous Security: 4th International Conference, UbiSec 2024, Revised Selected Papers},
  series = {Communications in Computer and Information Science},
  volume = {2469},
  pages = {174--190},
  year = {2025},
  publisher = {Springer},
  doi = {10.1007/978-981-96-4836-8_13},
  url = {https://doi.org/10.1007/978-981-96-4836-8_13}
}